The native app is real.
soldi's Expo app now builds in the cloud, installs on real phones, and passes its QA checklist — end to end, agent-driven, no laptop in the loop. Everything below is live and verified against staging only; production was never touched.
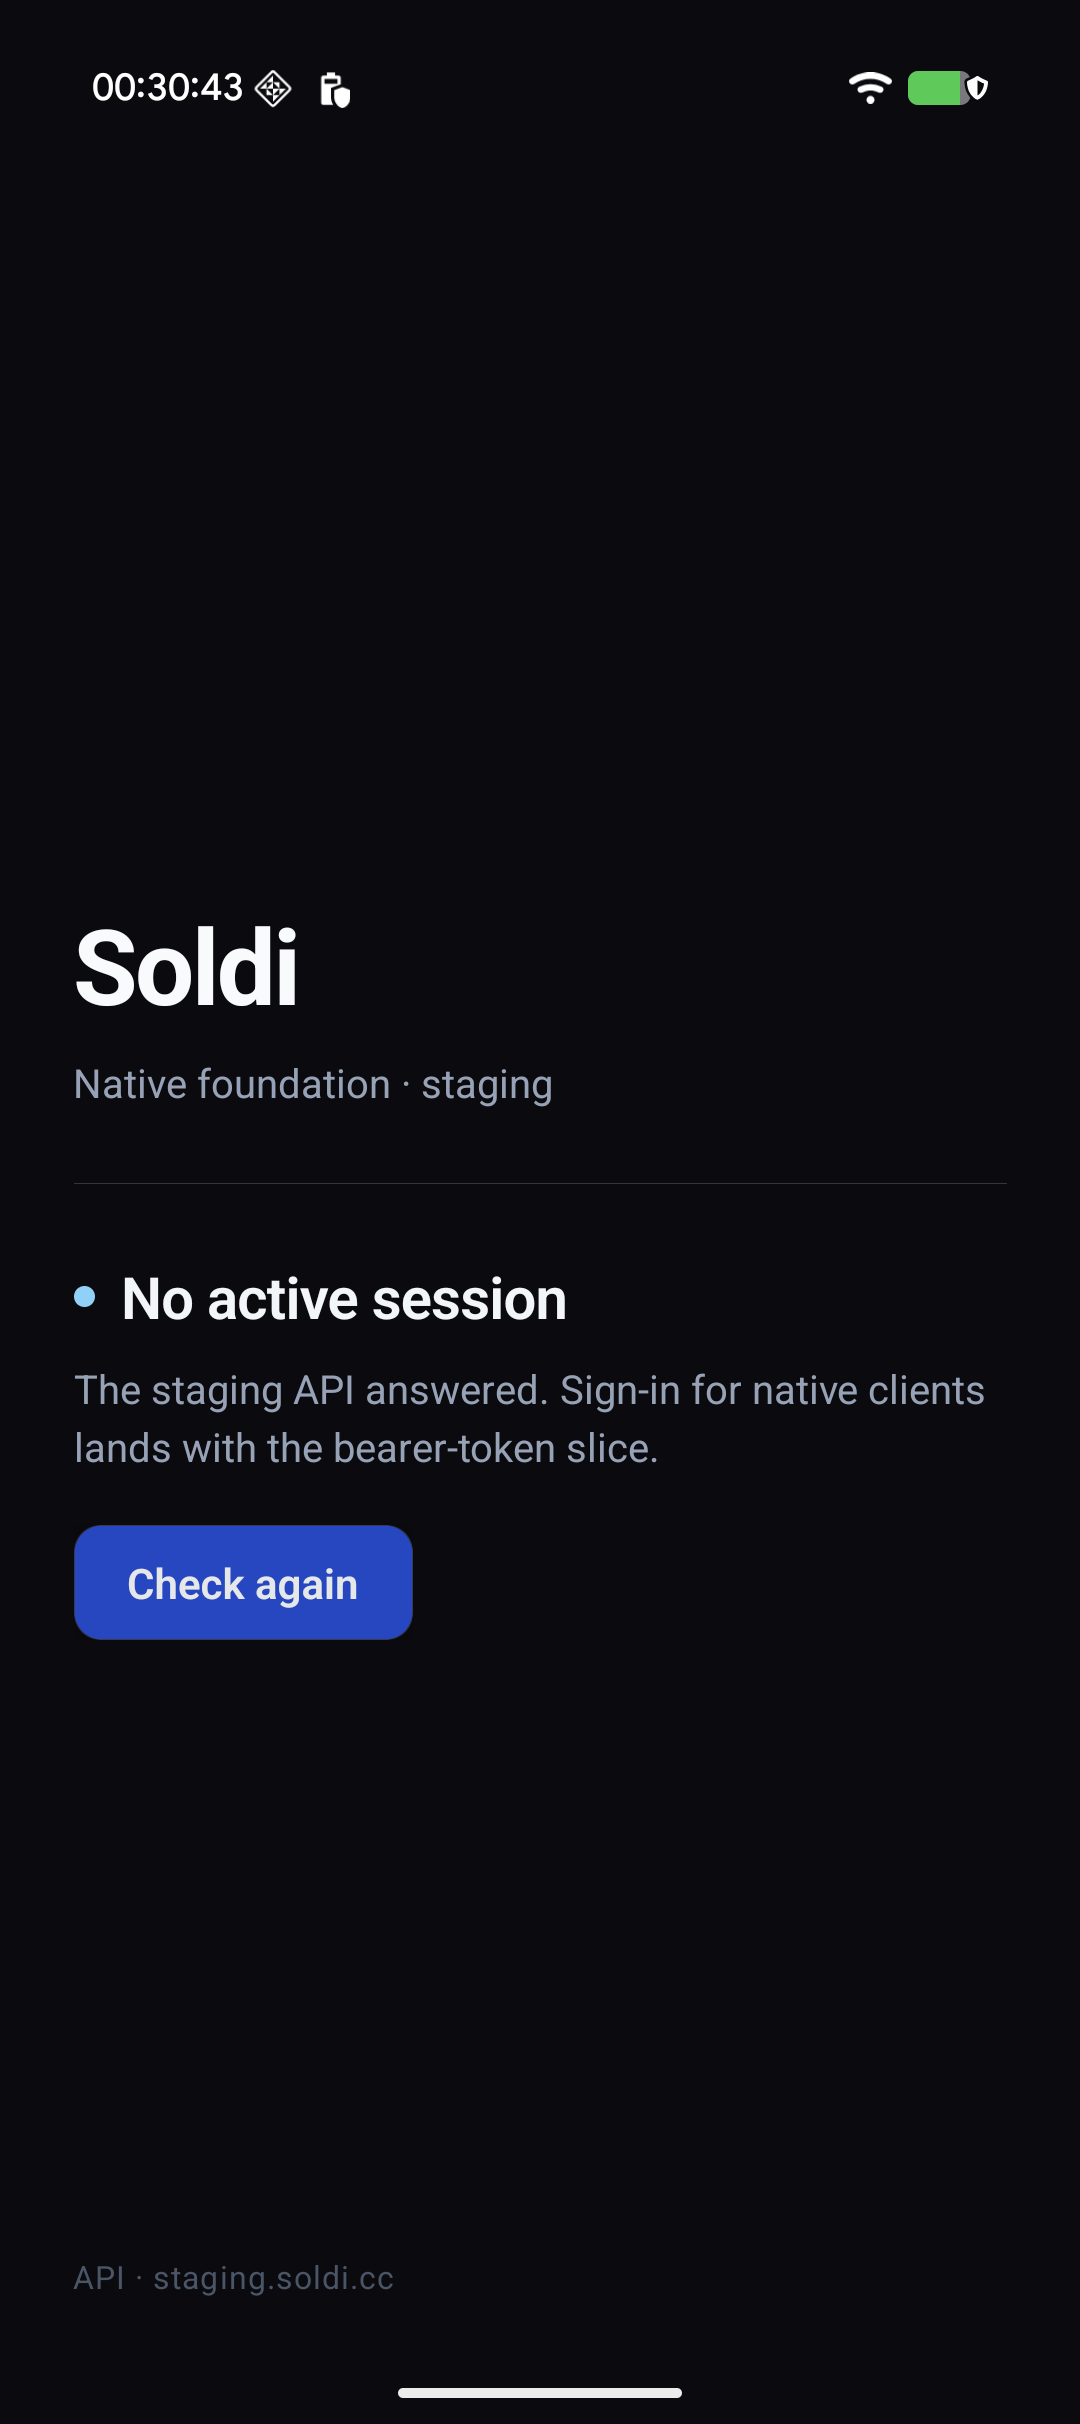
hosted device fleet, cold start
What you're looking at
A real, MDM-managed Pixel 10 in Mobile Next's hosted fleet, running the signed preview APK that EAS built from this repo. The app cold-starts clean, probes the staging API, and reports the honest signed-out state — “No active session” is the correct answer until the bearer-token sign-in slice ships.
The same install receives over-the-air JS updates: any
eas update --branch preview publish reaches this build on its next launch,
which makes the day-to-day iteration loop a ~2-minute publish instead of a ~20-minute build.
Checklist results
| Check | Result |
|---|---|
| Cold start — no redbox, staging footer visible | PASS |
| Signed-out shows “No active session”, not an error | PASS |
soldi:// deep link opens the app | PASS |
| Portrait lock holds under forced rotation | PASS |
| Background → return, no crash or duplicate probe | PASS |
| Accessibility — labeled, focusable 44dp controls | PASS |
| Airplane-mode retry/backoff · full TalkBack sweep | MANUAL |
eas update (~2 min OTA). Native change → eas build (~20 min signed APK).claude/mobile-mcp-spike carries the EAS config, session notes, and this page — review and merge (or say the word and a PR gets opened).eas build). Store submission stays human-gated.